Network security consultancy and practical security tooling

Secure network design, automation and assurance

SentryIQ helps MSPs and security teams design secure networks, monitor critical infrastructure, run SOC-ready workflows, review Cisco, Fortinet and Palo Alto environments, and automate evidence-led improvements.

assessment.yamlcontrols.jsonreport.md
assessment:
  source: pan-os-export.xml
  vendors: [PAN-OS, FortiGate]
  connectivity: none
  controls: 19
  frameworks:
    - PCI DSS v4.0
    - ISO/IEC 27001:2022
    - NCSC CAF

pipeline:
  parse -> reason -> map -> report
740-rule PA-7500 export~16% rulebase reduction opportunity identified
CiscoFortinetPalo Alto NetworksNetwork monitoringSOC / SIEM / EDR
19technical firewall controls checked during assessment.
4framework views across CE, PCI DSS, ISO 27001 and NCSC CAF.
16%rulebase reduction opportunity found in a 740-rule PA-7500 review.
100%offline assessment flow with no credentials, API access or cloud upload.

Security operating model

Monitoring, SOC and consultancy working together

SentryIQ keeps the operating model easy to understand: watch the environment, correlate the signals, then turn findings into remediation.

Monitor

Network monitoring

Monitor device health, secure edge availability, firewall signals and key network services so issues are visible before they become outages or security gaps.

  • Availability and health monitoring
  • Firewall and network signal review
  • Operational reporting and escalation paths

Improve

Consultancy and remediation

Use assessment evidence, monitoring signals and testing outputs to prioritise the changes that make the network more resilient.

  • Secure design and review
  • Pen-test findings triage
  • Remediation roadmaps

Consultant-led engineering

Security consultancy backed by repeatable tooling

SentryIQ combines senior network security consultancy with practical automation, offline assessment, network monitoring, SOC workflows, event correlation and backup tooling, so findings become decisions your team can act on.

Segmented network zonesSecure internet edgePolicy and profile assurance

What we do

Practical help for secure network programmes

Use SentryIQ when you need experienced network security consultants, clear implementation detail and tools that simplify assessment, backup, monitoring and response workflows.

Secure network design

Architecture and low-level detail teams can build from

Define trust boundaries, secure internet edge patterns, segmentation, remote access, routing and inspection decisions with the operational detail needed for delivery.

CiscoFortinetPalo Alto

Network automation

Repeatable workflows without losing control

Automate checks, backup routines, assessment inputs, reporting tasks and remediation preparation so consultants and engineers can spend more time on judgement.

Firewall review

Offline assessment with traceable evidence

Parse exports locally, explain shadowed and redundant rules, map findings to recognised frameworks and prepare client-ready reporting.

100% offline assessment19 technical controls4 assurance views

Backup tooling

Firewall configuration backup

ConfigVault is a built preview Windows collector for scheduled, encrypted Palo Alto Networks firewall configuration backup across MSP operating routines.

Monitoring and response

Network monitoring, SOC, SIEM and EDR support

Design monitoring routines, SOC triage paths, bespoke SIEM use cases, event correlation, ransomware protection workflows and EDR deployment patterns.

Testing and assurance

Pen testing, design review and remediation planning

Use SentryIQ for practical security consultancy across penetration testing coordination, findings triage, remediation planning and follow-up assurance.
Visibility

Understand where network controls really apply

Secure network work is rarely just one firewall. SentryIQ looks at how connectivity crosses users, branches, cloud services, data centres and internet edges, then translates that view into focused control improvements.

Global view

Internet edge and hybrid connectivity

Remote usersCloud regionSecure edgeSaaSBranchData centre
Control view

Firewall assurance heatmap

Control areaInternet edgeCoreCloudRemote
Policy scopeDefinedBroadMixedOpen
Inspection coveragePartialStrongMixedPartial
Application controlPortsHybridApp-IDMixed
Logging qualityClearUnevenClearSparse

Synthetic example only: used to show how findings can be prioritised without exposing customer data.

Introducing Sentry One

Offline firewall assessment, built for real engagements

Analyse Palo Alto PAN-OS and Fortinet FortiGate exports locally, surface rulebase and protocol risks, map findings to the frameworks clients ask about, and produce a professional report.

Offline assessmentMulti-vendorProtocol auditThreat-log analysis
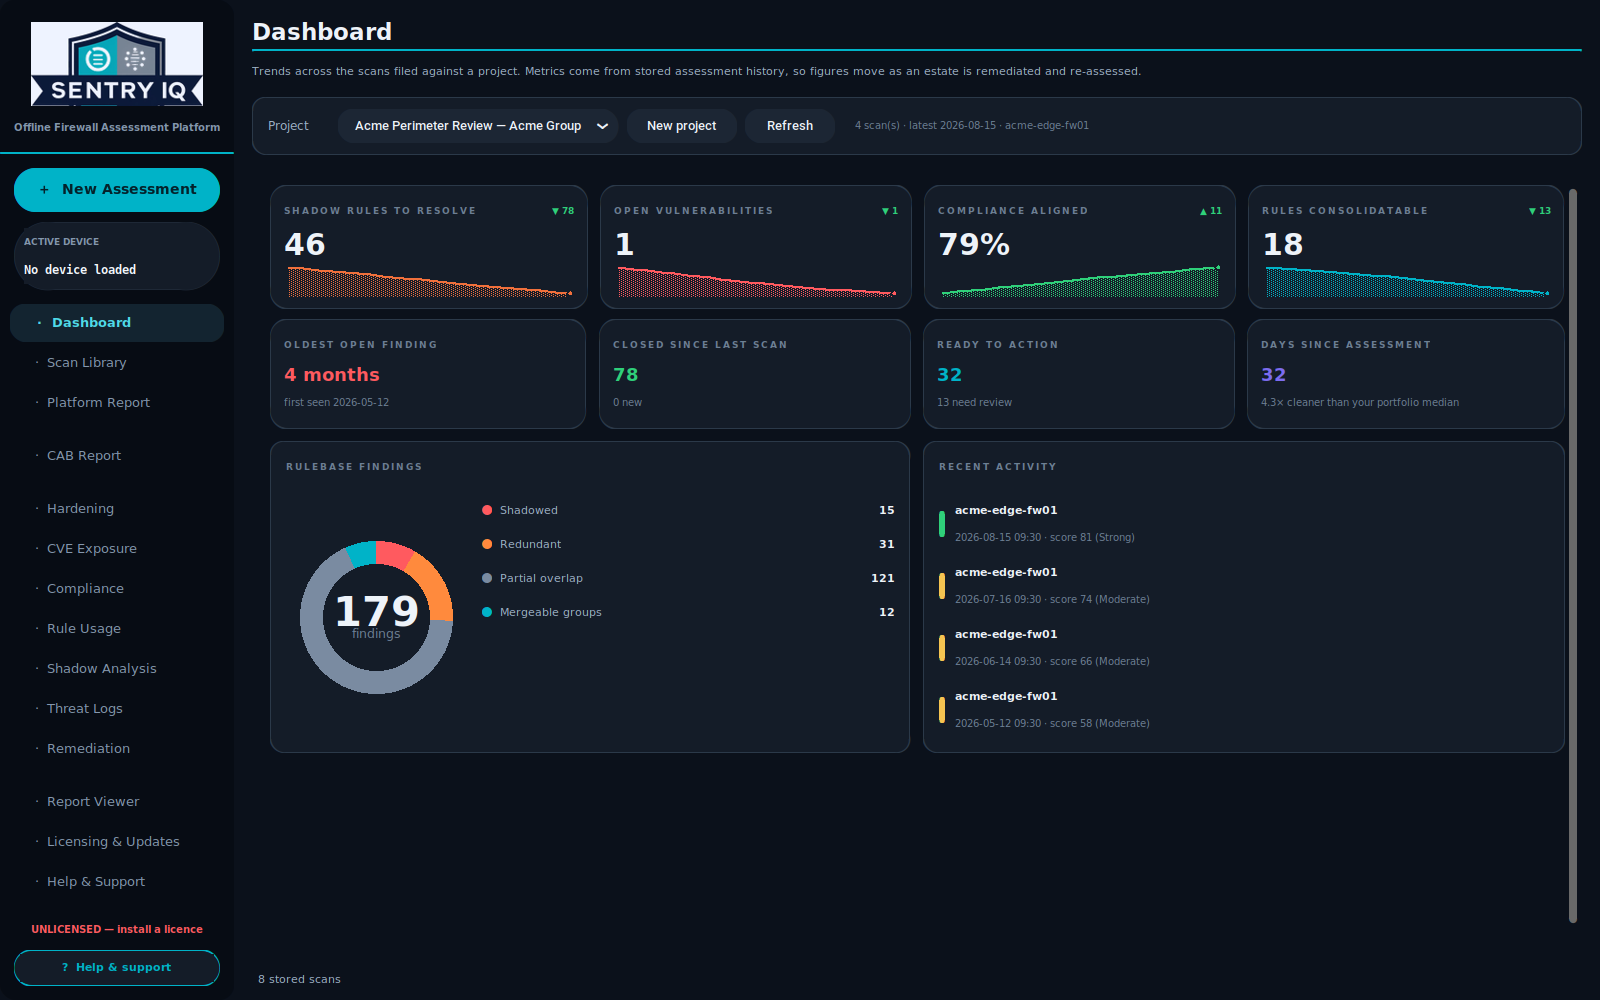
Sentry One dashboard showing firewall assessment metrics and rulebase findings
Assessment dashboardTrack rulebase findings, compliance alignment, vulnerability exposure and remediation progress over time.

ConfigVault

Firewall configuration backup for MSP operating routines

ConfigVault is a built preview Windows collector for scheduled, encrypted Palo Alto Networks firewall configuration backups with local folder, file share and Amazon S3 destination options.

Scheduled backupsEncrypted backup envelopesWindows collectorLocal management
ConfigVault overview showing healthy backups, the next scheduled run and five protected firewalls
ConfigVault overviewSee backup health, the next run and protected firewalls at a glance.

RouteGuard

Many alerts. One incident. Where it probably started.

RouteGuard correlates network, cloud and DDoS alerts with topology, routing and change evidence, giving operations teams an explainable investigation path.

Event correlationProbable starting pointChange evidenceAuditable confidence
RouteGuard incident showing 116 alerts correlated into one WAN failure
WAN incidentSee the initiating failure, dependent symptoms and recovery in one evidence-led incident.

Recognised benchmarks

Built for security. Mapped for compliance.

Sentry One relates technical findings to Cyber Essentials, PCI DSS v4.0, ISO/IEC 27001:2022 and the NCSC Cyber Assessment Framework, helping technical and governance teams work from the same evidence.

Framework views are indicative readiness mappings based on available firewall configuration evidence. They should be reviewed alongside wider organisational evidence and professional judgement.